
Google SSO (single sign-on) or Okta, which is better? At first glance, Google (more widely known for its search engine and cloud productivity tools) seems like an unlikely contender in the identity space. But that assumption underestimates the capabilities of Google’s identity offerings.
Okta leads the field for enterprises. Yet plenty of teams end up using Google as their identity provider for one simple reason: SSO is already included in Google Workspace, which they've usually got in place for Gmail and Drive anyway. The identity layer comes free with tools they already run.
Google SSO isn't purpose built as an identity solution so it has gaps next to Okta. But for SMBs, keeping Google as the IdP and layering identity governance on top covers the same core jobs at a fraction of the cost, and without migrating everyone to a new IdP.
This article helps you decide whether staying on Google SSO beats moving to an enterprise IAM suite. We compare aspects that drive the decision:
Setup process
Authentication capabilities
User provisioning and deprovisioning
Access control and management
Logging and audit reports
Google SSO vs. Okta: at a glance
Google SSO here means Google Workspace SSO. Okta references throughout are to Okta Workforce Identity Cloud (WIC), the workforce identity product, not Customer Identity Cloud (CIC / Auth0).
Dimension | Google SSO (Workspace) | Okta Workforce Identity Cloud (WIC) | Google SSO + AccessOwl |
|---|---|---|---|
Best for | Startups and SMEs already on Workspace | Enterprises with a dedicated identity team | Solo IT admins or early IT hires. Company <300 employees. |
Setup complexity | None if your team is already on Workspace | Months. Needs specialized IT personnel | Live in a few days on top of Workspace |
Authentication / MFA | Workspace identities, FIDO2, Authenticator | Broad MFA, adaptive/risk-based auth | Uses Google SSO; adds no auth of its own |
User provisioning coverage | SCIM for a small app catalog | Larger SCIM network, per-connector setup | Provisioning for 400+ apps without SCIM/SAML required |
Access control templates | Basic Workspace groups | Full RBAC, policies, attributes | Role and attribute based templates; Automatic mapping to HRIS |
Governance & audit readiness | Strong for Google apps, weak for 3rd party SaaS apps | Access reviews, certification campaigns | Access reviews and long-term records |
Pricing model | Included in most Workspace tiers | Per-user, per-module add-ons | Per-user, per-module add-ons, no SSO tax |
Trade-offs | Gaps with lifecycle automation and third-party audit | Large cost and setup overhead | Does not include device management or enterprise grade security authentication |
Google Workspace SSO vs. Google Cloud Identity: What’s the difference?
Google Cloud Identity is the dedicated IAM solution from Google. It's closer as a direct competitor to Okta than the Google SSO included in Google Workspace. Google Cloud Identity adds in device management and other identity governance features. Despite it being closer to feature parity to Okta, when most people discuss using Google SSO instead of Okta they are actually referring to the SSO features that already come with Google Workspace.
That's why this article focuses on Google Workspace SSO, the more commonly used, frictionless login option tied to your company’s Workspace accounts. This version of SSO is ideal for startups and smaller teams that don’t need extensive configuration, directory federation, or enterprise security controls. It delivers quick access across thousands of apps without the operational complexity of full-blown IAM software.
The biggest problem with Google SSO: User lifecycle management
Google Workspace does an excellent job of user authentication and authorization. Unfortunately, it falls short in other aspects of IAM.
We’ll cover this in more depth, but in a nutshell:
Access controls are basic and mostly tied to Workspace groups
There’s no built-in support for provisioning or deprovisioning users across external SaaS platforms
Reporting is sparse, especially when it comes to non-Google services
Automation is minimal, requiring manual approvals or IT bottlenecks
These limitations become real pain points as your company grows. Without a way to orchestrate user access across tools, you’re left with a patchwork of spreadsheets, email chains, and Slack DMs.
For many teams, this creates a dilemma: upgrade to a heavyweight tool like Okta, or find a middle-ground solution. That’s where AccessOwl comes in. By combining Google SSO with AccessOwl, you get centralized access approvals, user lifecycle automation, and a native slack integration without paying the “SSO tax” or deploying a dedicated IAM team.
"AccessOwl is a great alternative to solutions like Okta, which quickly become a cost trap". Marco Dubbert, CISO, Liqid
The biggest problem with Okta: Cost
Okta ticks all the boxes as far as IAM features, but its hidden costs may be too high for many startups and SMBs.
Here’s the issue: many SaaS vendors restrict SAML and SCIM access to enterprise-tier subscriptions. That means to use Okta effectively, you’ll also need to pay more for each SaaS app you use.
And sometimes the price increase is extreme. For example, the HubSpot standard plan costs $46 per month, but the enterprise plan with SSO costs over $3,600!
It’s called the SSO tax, and there’s a whole movement combating this exploitative practice.
All this is before you factor in Okta’s subscription cost.
$2 per user/month for SSO
$3 per user/month for MFA
$4 per user/month for lifecycle management
$9 per user/month for identity governance features
Google SSO and MFA, by contrast, are included in most Google Workspace tiers at no extra cost.
Check out our post on the true cost of Okta for a detailed overview of how the SSO tax affects your SaaS budget.
Okta vs. Google SSO: The complete breakdown
Here’s how Google SSO compares with Okta in terms of setup and functionality.
Setup
Google SSO requires no setup. The “Sign in with Google” option is already available on almost every SaaS service you use. Additionally, more than 3.8 million websites offer sign-in with Google. In contrast, Okta SSO configuration is a multi-step process that requires technical expertise. A simple misconfiguration can result in sign-in issues. It gets even trickier if a SaaS service lacks built-in SAML and SCIM, and you have to connect it manually to Okta using API keys. You’ll need a dedicated IT team to set up and manage Okta in your business.
Authentication
Google SSO uses Workspace identities and supports MFA via the Google Authenticator app or FIDO2 security keys.
Okta allows you to build a universal directory or connect external sources like Active Directory, Google, or Azure AD. It also supports a wider range of MFA factors: SMS, biometrics, push via Okta Verify, and contextual risk scoring.
In 2026, passwordless adoption is increasing across both platforms. Okta supports WebAuth and device trust, while Google is continuing to push passkeys as the default. If you want maximum flexibility, Okta is more powerful.
The bigger gap shows up in adaptive, risk-based authentication. Okta Workforce Identity Cloud (WIC) can adjust MFA (multi-factor authentication) requirements based on device posture, location, and risk signals, and it supports hardware tokens and biometrics. Google Workspace offers context-aware access on its higher tiers alongside FIDO2 security keys, and both are moving toward passwordless sign-in and passkeys as the default. If you run a regulated or complex environment where authentication decisions need to react to real-time risk, Okta's adaptive auth is a genuine strength and the right buy. For most teams on Workspace, context-aware access plus MFA covers the day-to-day need without the added layer.
Access control and management
This is where the divergence becomes clear. Google Workspace uses basic group structures to define access. You can restrict or permit app usage based on user groups, but you can’t define granular app-level permissions or roles.
Okta offers full RBAC (role-based access control), with attributes, policies, and dynamic provisioning flows. It’s designed for large, regulated environments with complex permission models. Still, tools like AccessOwl help bridge the gap. You can allow team members to request access directly in Slack, set approval workflows, and even define who can approve access to high-risk apps, without the rigidity of an enterprise IAM solution.
This creates a big list of variables that could be simplified by defining specific roles and assigning access rights and permissions to those roles.
The good news is that coupling Google SSO with AccessOwl eliminates the complexities of access management by allowing employees to request access right in Slack. AccessOwl then forwards the requests to the right stakeholders for approval.
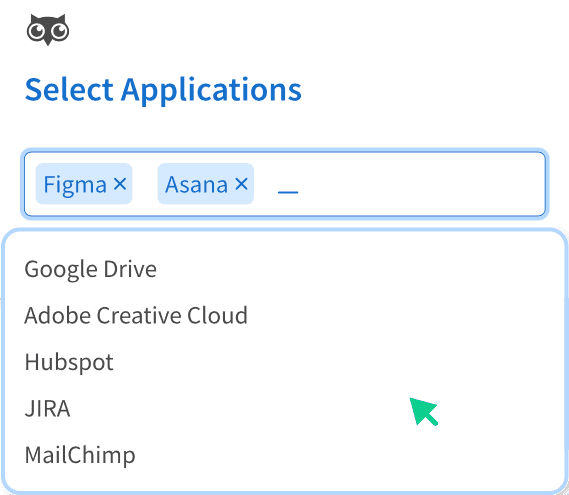
You can also set up auto-approval for low-risk applications, or multi-step approval flows with several stakeholders for high-risk applications. This option is available only on Okta Identity Governance, which starts at $9 per user.
User provisioning and deprovisioning
Both solutions support SCIM provisioning, but Google Workspace offers support for a small number of SaaS applications.
Consequently, you may need to manually provision users to your SaaS apps and manually delete them if they leave the company. This can quickly become overwhelming, especially if you’re using multiple SaaS solutions.
Okta integrates with a larger number of SaaS apps via SCIM, allowing you to automatically create, update, or remove accounts based on directory rules.
However, you still need to configure each connector—and some SCIM-enabled SaaS apps require enterprise-tier plans to unlock that functionality.
There’s good news: AccessOwl can take care of account creation, changes, and deletion without the SCIM protocol. It supports more than 100 tools, including Google Workspace, Notion, Slack, and Atlassian.
Better yet, you can integrate AccessOwl into your onboarding and offboarding flows so that it automatically creates or deletes user accounts for you.
Monitoring and reporting
Google’s reporting is excellent for Google products. You can view Drive activity, Admin console access, and login logs. But, when it comes to third-party SaaS tools, the audit trail is sparse.
Okta offers more consistent access logs across your stack, but the default retention is only 90 days unless you pay extra or export to a SIEM platform.
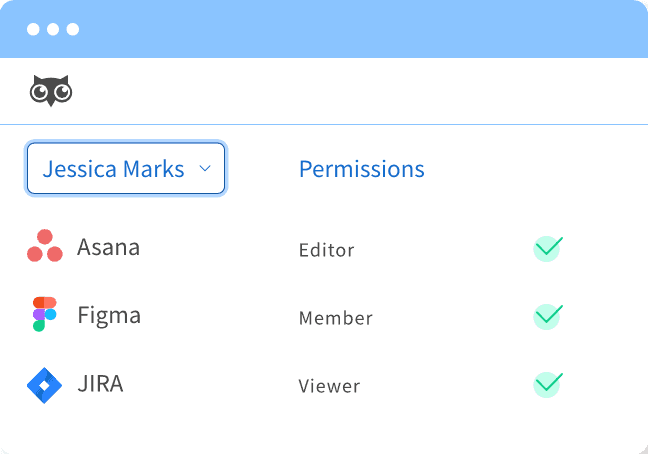
This is where AccessOwl comes in. It acts as the single source of truth for all applications, accounts, roles, and permissions, and it allows you to download access reports at any time.
On its end, Okta also offers solid access tracking and lets you easily download reports necessary for proving compliance.
However, it retains activity logs for only 90 days. You’ll need to find another way to store the logs for future use.
The middle ground: do 50-500 person teams need Okta?
Most 50 to 500 employee companies don't have to commit to Okta outright to get the governance they need. The pragmatic middle ground is Google SSO for authentication plus AccessOwl for lifecycle automation, access requests and approvals in Slack, and access reviews. That pairing covers most of Okta's governance value without the enterprise cost or a dedicated identity team to run it.
If you're the first or only IT hire, the real gap you're feeling is rarely authentication. It's automation: provisioning, deprovisioning, and audit-ready access records across your whole SaaS stack. Google SSO already handles the login layer, so a governance layer on top closes the lifecycle gaps that matter today. As you scale and add a dedicated identity team, revisiting a full IAM suite makes sense.
If compliance is a priority (e.g., SOC 2, ISO 27001), having long-term records of who had access, who approved it, and when they lost it is no longer optional but essential.
Which one should you use? The verdict.
On paper, Okta may seem like an obvious next step in your IAM journey. It’s a full-fledged solution for taking care of authentication, authorization, access management, and reporting.
In real life, however, it’s not as straightforward.
First, there’s the initial cost to procure Okta. SSO, MFA, lifecycle management, and identity governance are all offered as different solutions that you purchase separately. Then there is the SSO tax to worry about.
Moreover, the setup and management of Okta is a complex process that requires a dedicated IT team. Google SSO, on the other hand, requires no initial setup, and it’s available for free with Google Workspace.
Conclusion: Okta is a great solution if you’re planning to hire a dedicated IT team and you expect to upgrade to enterprise subscriptions for all your SaaS apps.
If you don’t have a dedicated IT department, or the budget for the more expensive enterprise plans, then Google Workspace coupled with a tool such as AccessOwl might be a better alternative. You’ll still enjoy all of Okta’s benefits, but without the complex setup processes and hidden costs.
FAQ
Which is better: Okta or Google SSO?
Okta is an excellent all-around identity provider, but it comes with hidden costs. Google SSO, on the other hand, is free but lacks some key features of lifecycle management. However, if you use Google SSO, you can couple it with AccessOwl to enjoy many of Okta’s benefits without the high cost and setup hassle.
Is Google SSO free?
Yes. Google Workspace users can set up Google SSO coupled with MFA at no cost. This allows users to sign in to your SaaS tools without needing to create multiple login credentials.
How secure is Google SSO?
Google SSO helps boost business security by eliminating the need for users to have multiple passwords for multiple accounts. Consequently, you don’t have to worry about cybercriminals exploiting weak or reused passwords to infiltrate your business. Google SSO also supports MFA, which adds another layer of protection on top of standard sign-in.
What are the disadvantages of Okta?
Okta’s biggest disadvantage is cost. On top of the usual upfront fees (subscription, deployment, and admin training), choosing Okta also means paying the SSO tax — the extra fees or forced upgrades demanded by SaaS providers for SAML and SCIM support.
What are the disadvantages of Google SSO?
The biggest problem with Google SSO is the management of third-party users after authentication. However, instead of switching to SAML and SCIM and incurring unnecessary costs, you can combine AccessOwl with Google SSO and enjoy both identity and access management.
Does Google support SAML-based SSO?
Yes, Google Workspace supports SAML based SSO.
What authentication features do Google SSO and Okta offer?
Google Workspace SSO uses your Workspace identities and supports MFA (multi-factor authentication) through the Google Authenticator app, FIDO2 security keys, and context-aware access on higher tiers. Okta Workforce Identity Cloud (WIC) adds a wider set of MFA factors along with adaptive, risk-based authentication that adjusts requirements based on device posture, location, and risk signals. Both are moving toward passwordless sign-in and passkeys as the default.
How do Google SSO and Okta handle user provisioning?
Both support SCIM provisioning, but Google Workspace covers only a small app catalog, so most third-party SaaS accounts are created and removed by hand. Okta Workforce Identity Cloud connects to a larger SCIM network, though each connector needs setup and some SaaS apps gate SCIM behind enterprise-tier plans. AccessOwl closes that gap for Google SSO users: it provisions and deprovisions across 400+ tools so you get broad automated coverage without requiring SCIM or paying the SSO tax, and it plugs into your onboarding and offboarding flows to create and remove accounts automatically.